Privacy & access
NetBird
WireGuard-based private network that connects your machines and self-hosted services without port forwarding.
Release notes / v0.83.0
Released 2026-11-12. Snapshot from the included release data, not a live check.
# Release Notes for v0.83.0 ## ⚠️ Breaking changes: profile ownership and daemon access control Each profile now has an owner, and local users can control only their own profiles as the daemon has a new IPC authorization layer. Single-user desktops and headless peers registered with a setup key and auto-start (the default) need no action. They reconnect on their own after the upgrade. Act only if one of the cases below applies to you. [#7407](https://github.com/netbirdio/netbird/pull/7407)…
Read the full release notes on GitHub ↗Available on these platforms
Mobile VPN clients join a NetBird network. This is not a claim that the management server runs on iOS or Android; mobile features and routing behavior can differ.
Compatibility details and official sources
Official availability checked 2026-11-12. Availability is not feature parity. The recorded release and license refer to the linked source project; separate clients can differ. No install or compatibility test was run.
Before you install
A private network over WireGuard, no open ports.
- What does it run on?
- A management server you host (or the project's hosted service) plus a small client on each machine. Peers reach each other directly by name, wherever they are.
- Where is my data?
- Peer registry, groups, access rules and DNS live on your management server; traffic flows directly between your machines over WireGuard.
- What will I maintain?
- The management stack and client updates. The admin dashboard handles peers, groups, access rules and routes - plan those before inviting a fleet.
Advice and funding routes source-checked November 12, 2026. Researched, not an install or restore test. Installation source ↗ · Report a correction
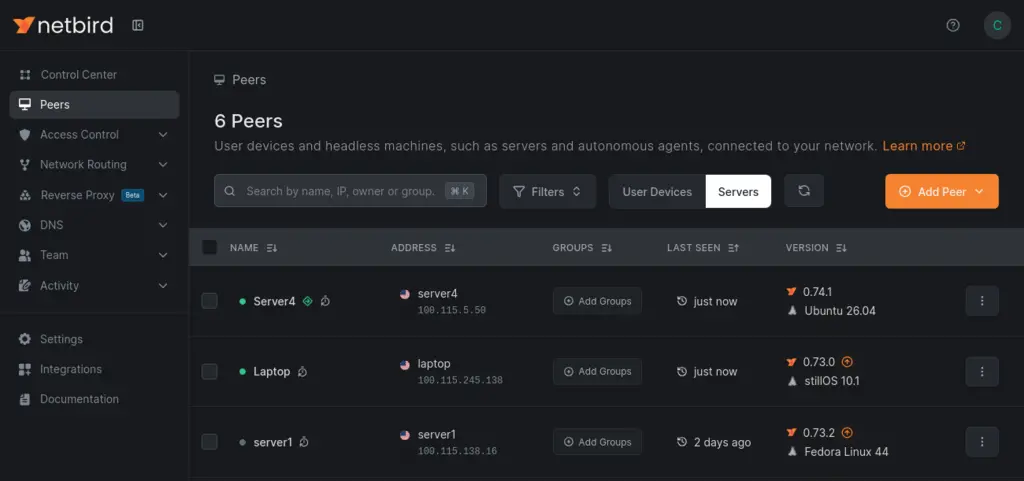

NetBird builds a private network between your machines over WireGuard. Once a laptop, a home server and a cloud VM join, they reach each other directly by name, wherever they are, with no open ports or port forwarding on any router. An admin dashboard manages peers, groups, access rules, DNS and routes to whole networks through a routing peer.
The client and most of the codebase are published under the BSD-3-Clause license; the self-hosted server components (management, signal, relay and the combined deployment) are AGPL-3.0. NetBird Cloud is the company’s managed version for anyone who would rather not run the control plane.
Quick start
Verified against NetBird’s own documentation on November 8, 2026; we haven’t run these setups ourselves.
Unlike most tools here, a NetBird control plane has to be publicly reachable: peers, TLS and relay traffic expect a real domain and open ports. Upstream’s supported self-host route is its installer script on a public VM (at least 1 CPU and 2 GB RAM) with a domain pointing at it and TCP ports 80 and 443 plus UDP 3478 open:
curl -fsSL https://github.com/netbirdio/netbird/releases/latest/download/getting-started.sh | bashThe script asks which reverse proxy to use (Traefik by default, with
options for an existing Traefik, Nginx, Nginx Proxy Manager or an external
Caddy) and generates a docker-compose.yml plus config files you manage
with docker compose afterwards. When it finishes, open
https://netbird.example.com (your domain) and create the first admin
account on the /setup page, which only exists until the first user does.
NixOS
nixpkgs ships a full server stack module:
services.netbird.server = {
  enable = true;
  domain = "netbird.example.com";
  enableNginx = true;
};
Run sudo nixos-rebuild switch, then create the admin account at your
domain. The module enables the dashboard, management API and signal
service together; relay and coturn options live under the same
services.netbird.server namespace. Machines that only join a network
need the client instead, services.netbird.
Why it’s listed
Every tool in this directory needs a safe way to be reached from outside your network. NetBird provides that path without exposing ports to the internet, and its self-hosted control plane keeps the whole setup in your own hands.
Documentation
NixOS · WireGuard-based private network that connects your machines and self-hosted services without port forwarding. Paste into your AI assistant. It may only be able to guide you. Review changes before running anything.
Researched, not run by the Index. Checked 2026-11-12. No AI account or connection is needed here.
Read or copy the prompt manually
Tags: Networking
Want help running it? Ask FOSSadmin about hosting and maintenance ↗